

We find your exposed credentials, and fix them
Passwords, API keys and tokens end up scattered across the platforms your people work in. We find them, score them by risk, and take responsibility for getting them fixed alongside your relevant teams. Delivered as a service, with no platform for you to license or maintain.
Talk to us
22% of breaches begin with compromised credentials, the most common initial access route for the second year running (Verizon 2025 Data Breach Investigations Report)
The gap between finding exposed data and fixing it.
Credentials get pasted into a Confluence page, a Jira ticket, a Teams chat, and take on the permissions of wherever they landed rather than the sensitivity of what they unlock.
Sensitive data spreads this way through ordinary work, out of sight of the security team, and credentials remain one of the most common ways into an organisation.
Finding it is not the hard part, its what you do with that information. A discovery exercise ends with thousands of findings, scattered across teams that do not own them and each needing a different fix.
Without someone accountable for closing them, most simply stay where they are, found and unfixed.

What we do: One service, from finding it to fixing it.
We deliver this as a managed service using our own detection and validation engine, tuned to your environment. There is no platform for you to license, learn or maintain. Here’s how it works:
Agree what sensitive data means to you
Sensitive data is not a fixed term. We agree the definition and the locations to scan up front, whether that is passwords, keys and tokens, personal data, or other patterns specific to your business.

Find it across your platforms
Our engine searches the places people store and share information: SharePoint, OneDrive, Confluence, Jira, Teams and file shares.
Detection is tuned to your environment and refined to keep false positives down, which is where off-the-shelf tools tend to drown teams in noise.

Score every finding by risk
Findings are rated against criteria you agree, so the credential exposing customer data is separated from the low-priority housekeeping.
An unworkable spreadsheet becomes a short list of what genuinely matters.

Remediate, end to end
We work alongside the teams who own the systems to ensure findings are closed and take accountability for driving that process rather than handing you a backlog.
Depending on context that means relocating a credential to a secrets store, rotating it, redacting and restricting access, or removing it outright, working alongside the teams who own the systems.
Where the cause is behavioural, we work upstream so it stops recurring.
Report the risk coming down
Reporting through the engagement tracks outstanding risk over time, so your board and your auditors can see the exposure shrinking rather than a one-off snapshot.
Why teams choose this service
- Remediation process ownership. We work with the relevant teams to ensure findings are closed and are accountable for this process.
- Tuned to you. Detection is built around your environment and your definition of sensitive data, not a generic pattern set you are left to configure.
- False positives handled. The common complaint about DLP tools for this use case is the noise. We take responsibility for the quality of the output rather than flooding a dashboard.
- No lock-in, no licence. Nothing to buy that becomes shelfware, no specialist platform skills to hire for, no vendor to be tied to. You buy the outcome.

Find out where your exposure sits
Talk with the people who do this work. We’ll show you where sensitive data usually hides in environments like yours, the areas most worth checking, and what finding and fixing it would involve.
You’ll leave with a clearer view of your risk than when you started.



Tech Blog, Whitepapers & Guides
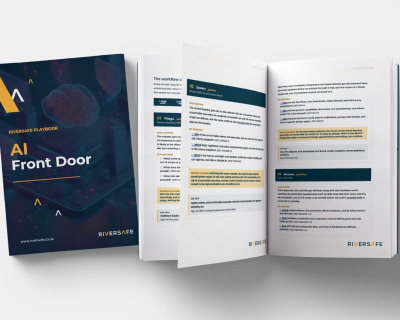
The AI Front Door: A Six-Step Workflow For Governing Every AI Tool Your Organisation Adopts
by Suresh Ramasubbu


Resources, Whitepapers & Guides
The C2/RMM Problem: Why AI guardrails fail on framing, not capability
by Naveen Jalagadugu


Case Studies, Resources
Building a Future-Ready Target Operating Model for JD Sports
by Patrick Morris